Prime Hunt
Automate retrospective threat search across your security stack – query data where it lives or bring the exported log files.
Used Daily by 11,000+ SOC Teams


“It Made a Security Operations Life Easier”
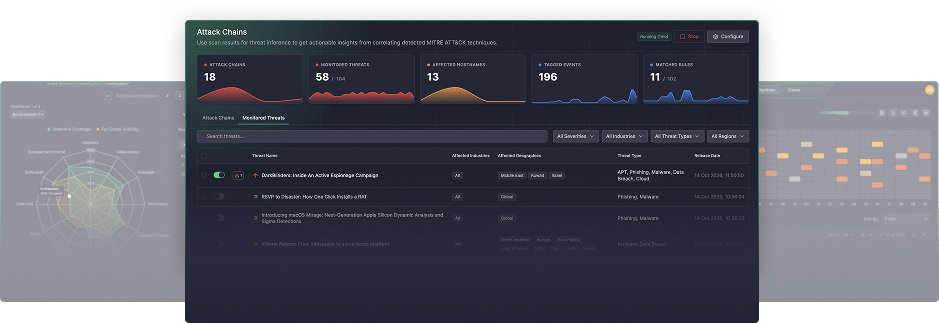
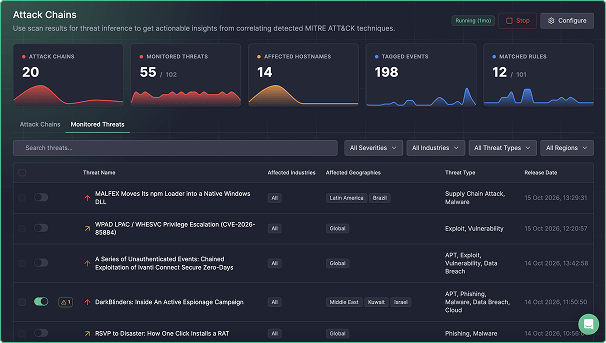
Attack Chains
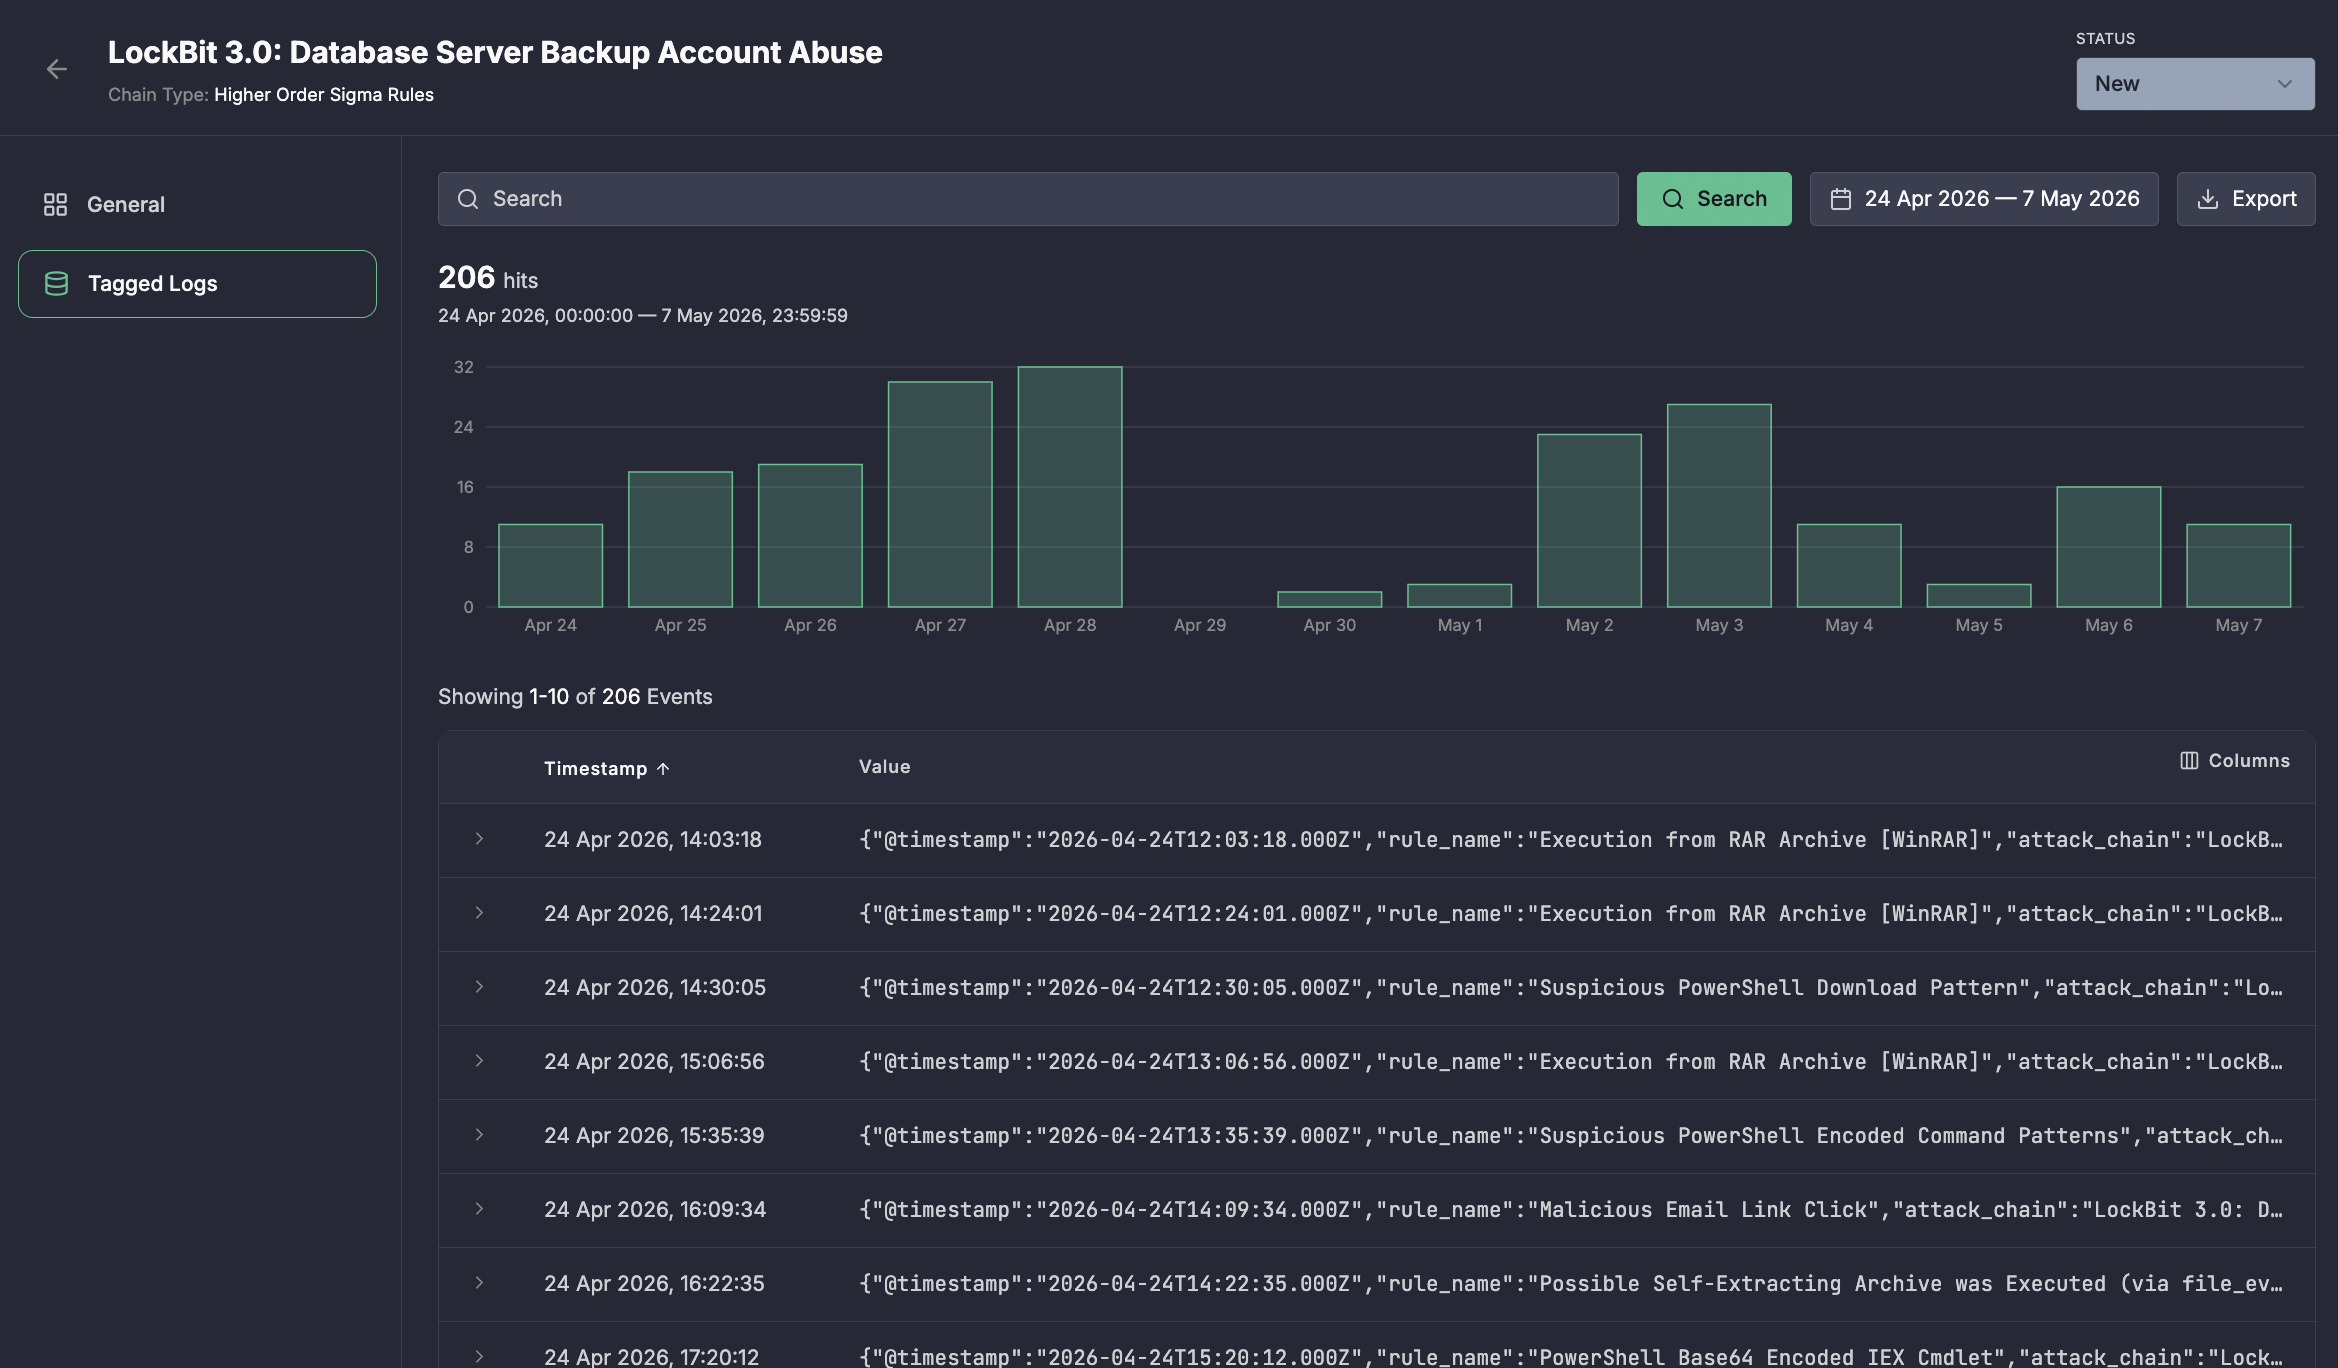
- AI groups related scan hits into chains that may represent a multi-step attack
- Each chain comes with an AI summary, ATT&CK techniques, threat actors, a timeline, and recommended response
- Tune the correlation window (1–24 hrs), the lookback (up to 365 days), and the match threshold to your environment
Data Audit
- Map the logs you actually collect to MITRE ATT&CK and see your real coverage
- Find blind spots: techniques you can’t detect because the telemetry isn’t there
- Prioritize what to start logging next, based on evidence instead of guesswork
Content Audit
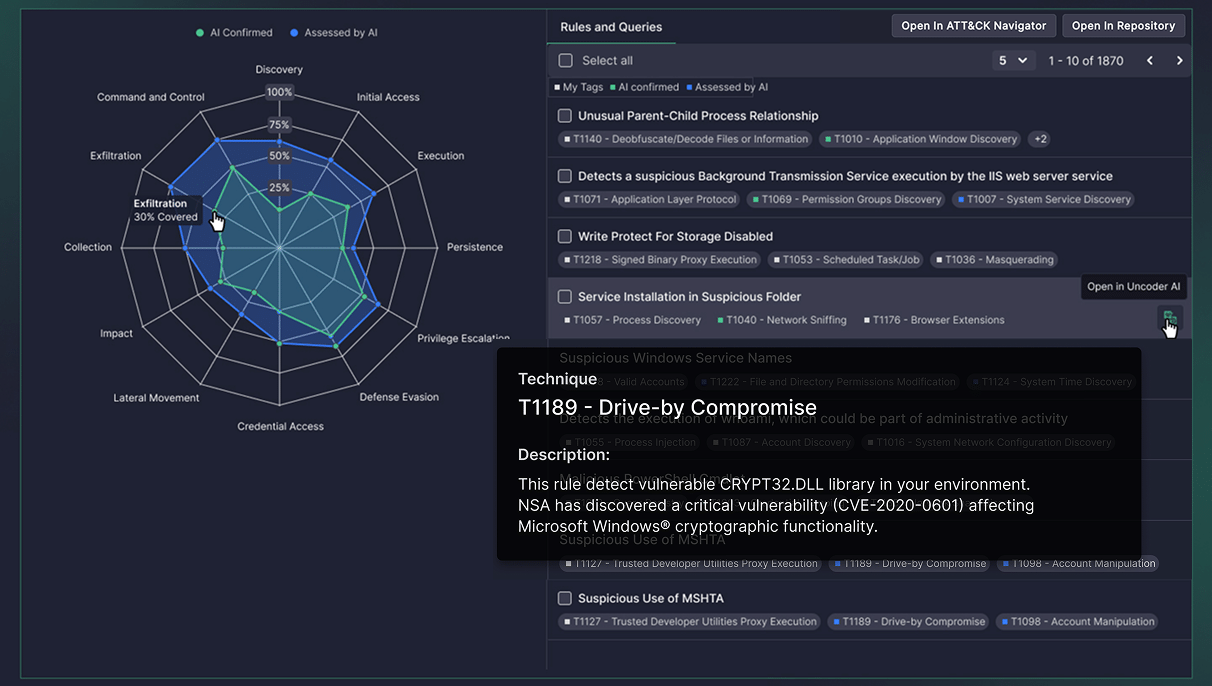
- Auto-map your existing rules and queries to ATT&CK with SOC Prime’s AI models
- Run it against a repository before you connect any SIEM
- See overlap and gaps across your detection library at a glance
SIEM Data Scan
- Search your historical data with Sigma rules translated for your platform. No query writing needed.
- Threat Hunting mode automates routine hunts and correlates findings with ATT&CK and threat intel
- Rules for Alerting mode finds the rules that fire in your environment, so you deploy fewer, higher-signal alerts
Log Event Analysis – LogTotal
- Drop in a log file (.log, .json, .evtx, and more, up to 3 GB) and analyze it without a SIEM connection
- Sanitize hostnames, IPs, credentials, and file paths before anything goes further
- Match events against SOC Prime’s detection rule set and correlate the results into Attack Chains
Query Where Data Lives
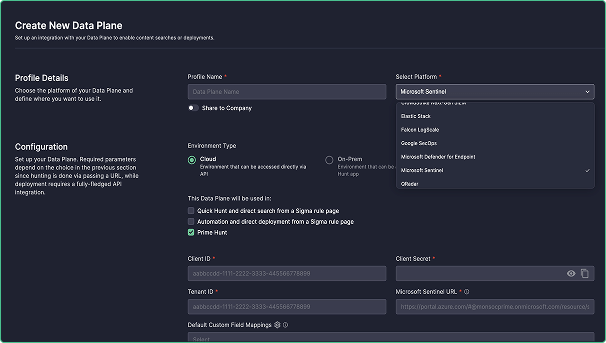
- API connections to 10 cloud platforms, plus apps for on-prem QRadar, Splunk, Elastic, and LogScale
- Scan up to 5 Data Planes at once
- Exclude noisy rules from future scans, and export scan results as a PDF report


OVER 12
Vendor Integrations
Countries
155
Organizations
11,000+
Users
60,000+
Trusted by Enterprise SOC Teams








